DeepSeek Harness Plugins · admin-security
Plugins that extend DeepSeek Harness (DSH) with vision, workflows, memory, web tools and more.
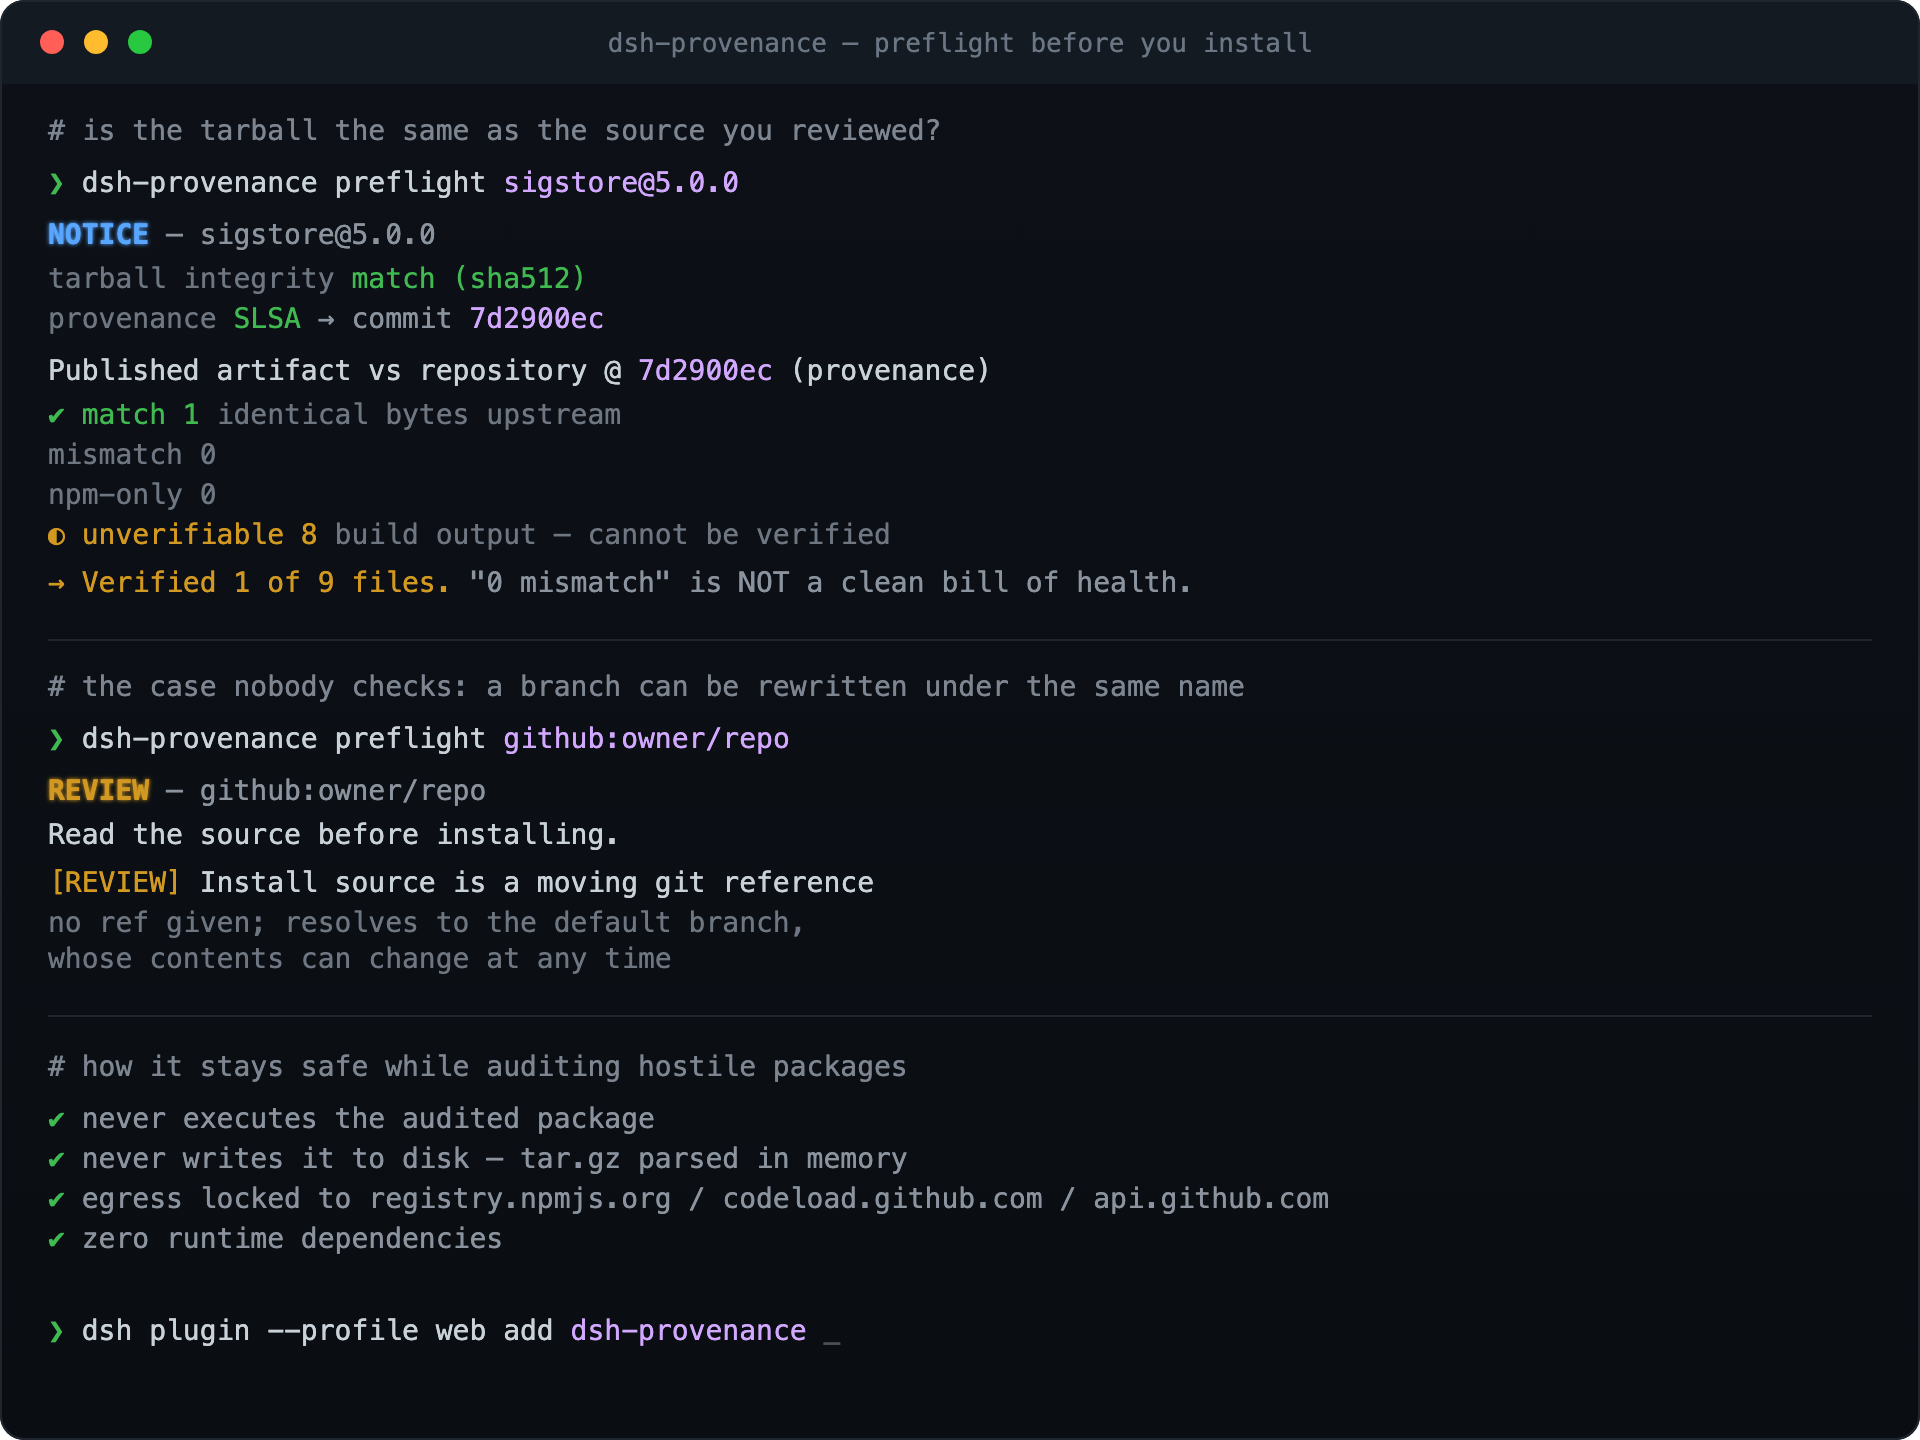
A supply-chain provenance preflight for DeepSeek Harness plugins that cross-checks the npm registry, upstream repository, and wire bytes to catch injected install hooks before they execute.
Transaction-based plugin cleanup engine for DeepSeek Harness with crash recovery, hash-chain audit, Bayesian oracle prediction, and chaos drills for verifiable, reversible, auditable deletion.
DSH enterprise governance suite: policy gates (allow/deny/ask), structured JSONL audit logs, and per-agent token period quotas persisted under DSH_HOME/gov/.
Security gate for DeepSeek Harness: 60 static signature rules detect malicious plugin code, and destructive-command guards prevent rm -rf-class accidents before installation.
An auto-approval guard for DeepSeek Harness that lets safe commands run freely while always prompting for destructive operations, with two modes and 11 per-category switches.
A login wall and reverse proxy that lets external browsers securely reach a cloud-deployed DeepSeek Harness via /dsh on port 8080.
Per-project LLM token usage and RMB cost breakdown (cached/uncached input, output) with a sidebar panel in DSH web, zero runtime dependencies.
Acquires an exclusive lock on the DSH_HOME directory at startup and aborts loudly when another live dsh server is already bound to the same data root, preventing silent session-log corruption.
Packages DSH platform capability boundary rules into a single loadable skill, helping developers assess channel support, API filesystem limits, and plugin lifecycle constraints before writing a plugin.
Merges plugin recommendation, quality scoring, security audit, and environment recipes into one unified decision tool.
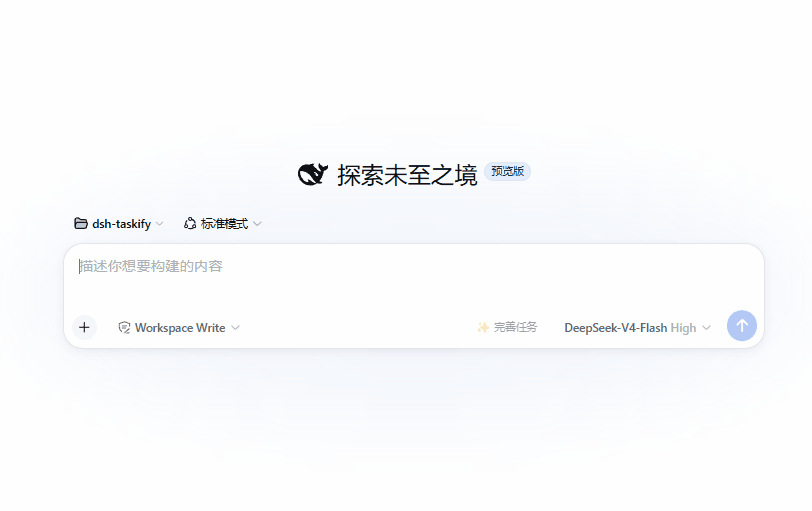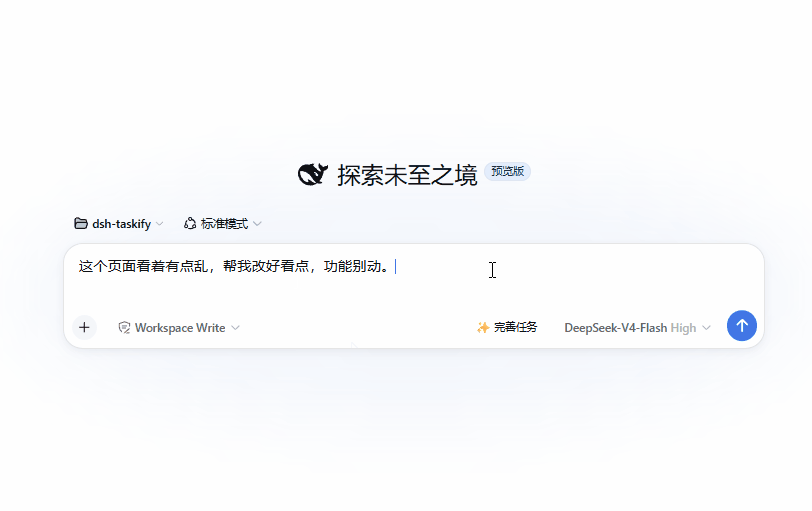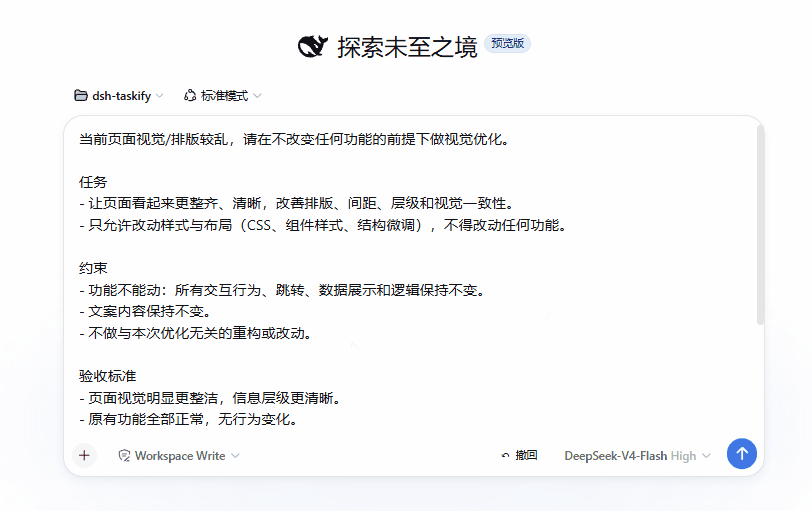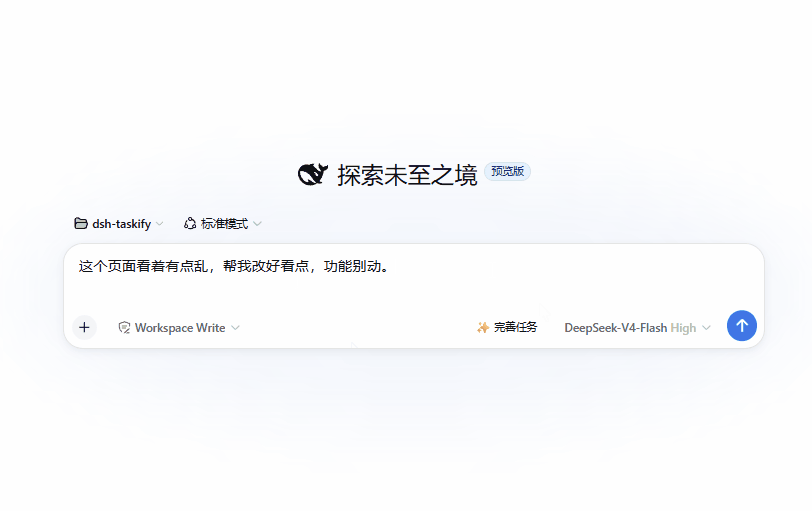
Pin a task scope with Focus and lock user-stated hard constraints with Persistent Anchors, keeping execution boundaries alive across turns without rewriting the original prompt.
Bridges VulnClaw and DeepSec into DSH with 18 security tools and a graphical workbench for code audit and authorized pentesting, with zero third-party runtime dependencies.