DeepSeek Harness Plugins · admin-security
Plugins that extend DeepSeek Harness (DSH) with vision, workflows, memory, web tools and more.
Adds a per-session permissions tab that enforces tool-level access via the strictest intersection of official presets, Claw hard caps, and Agent policies.
Returns structured blame-avoidance methods based on given parameters; pure Node.js with no network dependency.
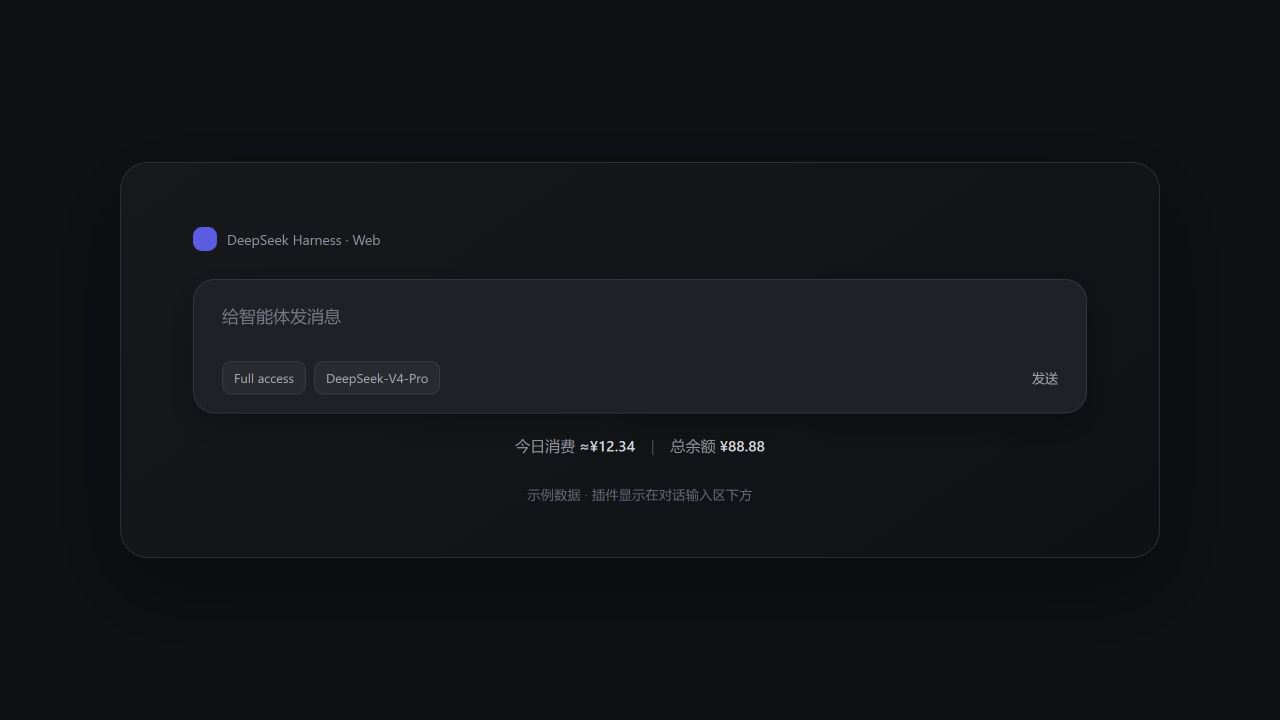
Shows estimated daily spend and account balance right in the DSH chat area, auto-refreshing every 3 minutes.
Reviews installed plugins before enabling or updating them via static scanning and semantic analysis, detecting remote-execution and exfiltration risks with user confirmation gates.
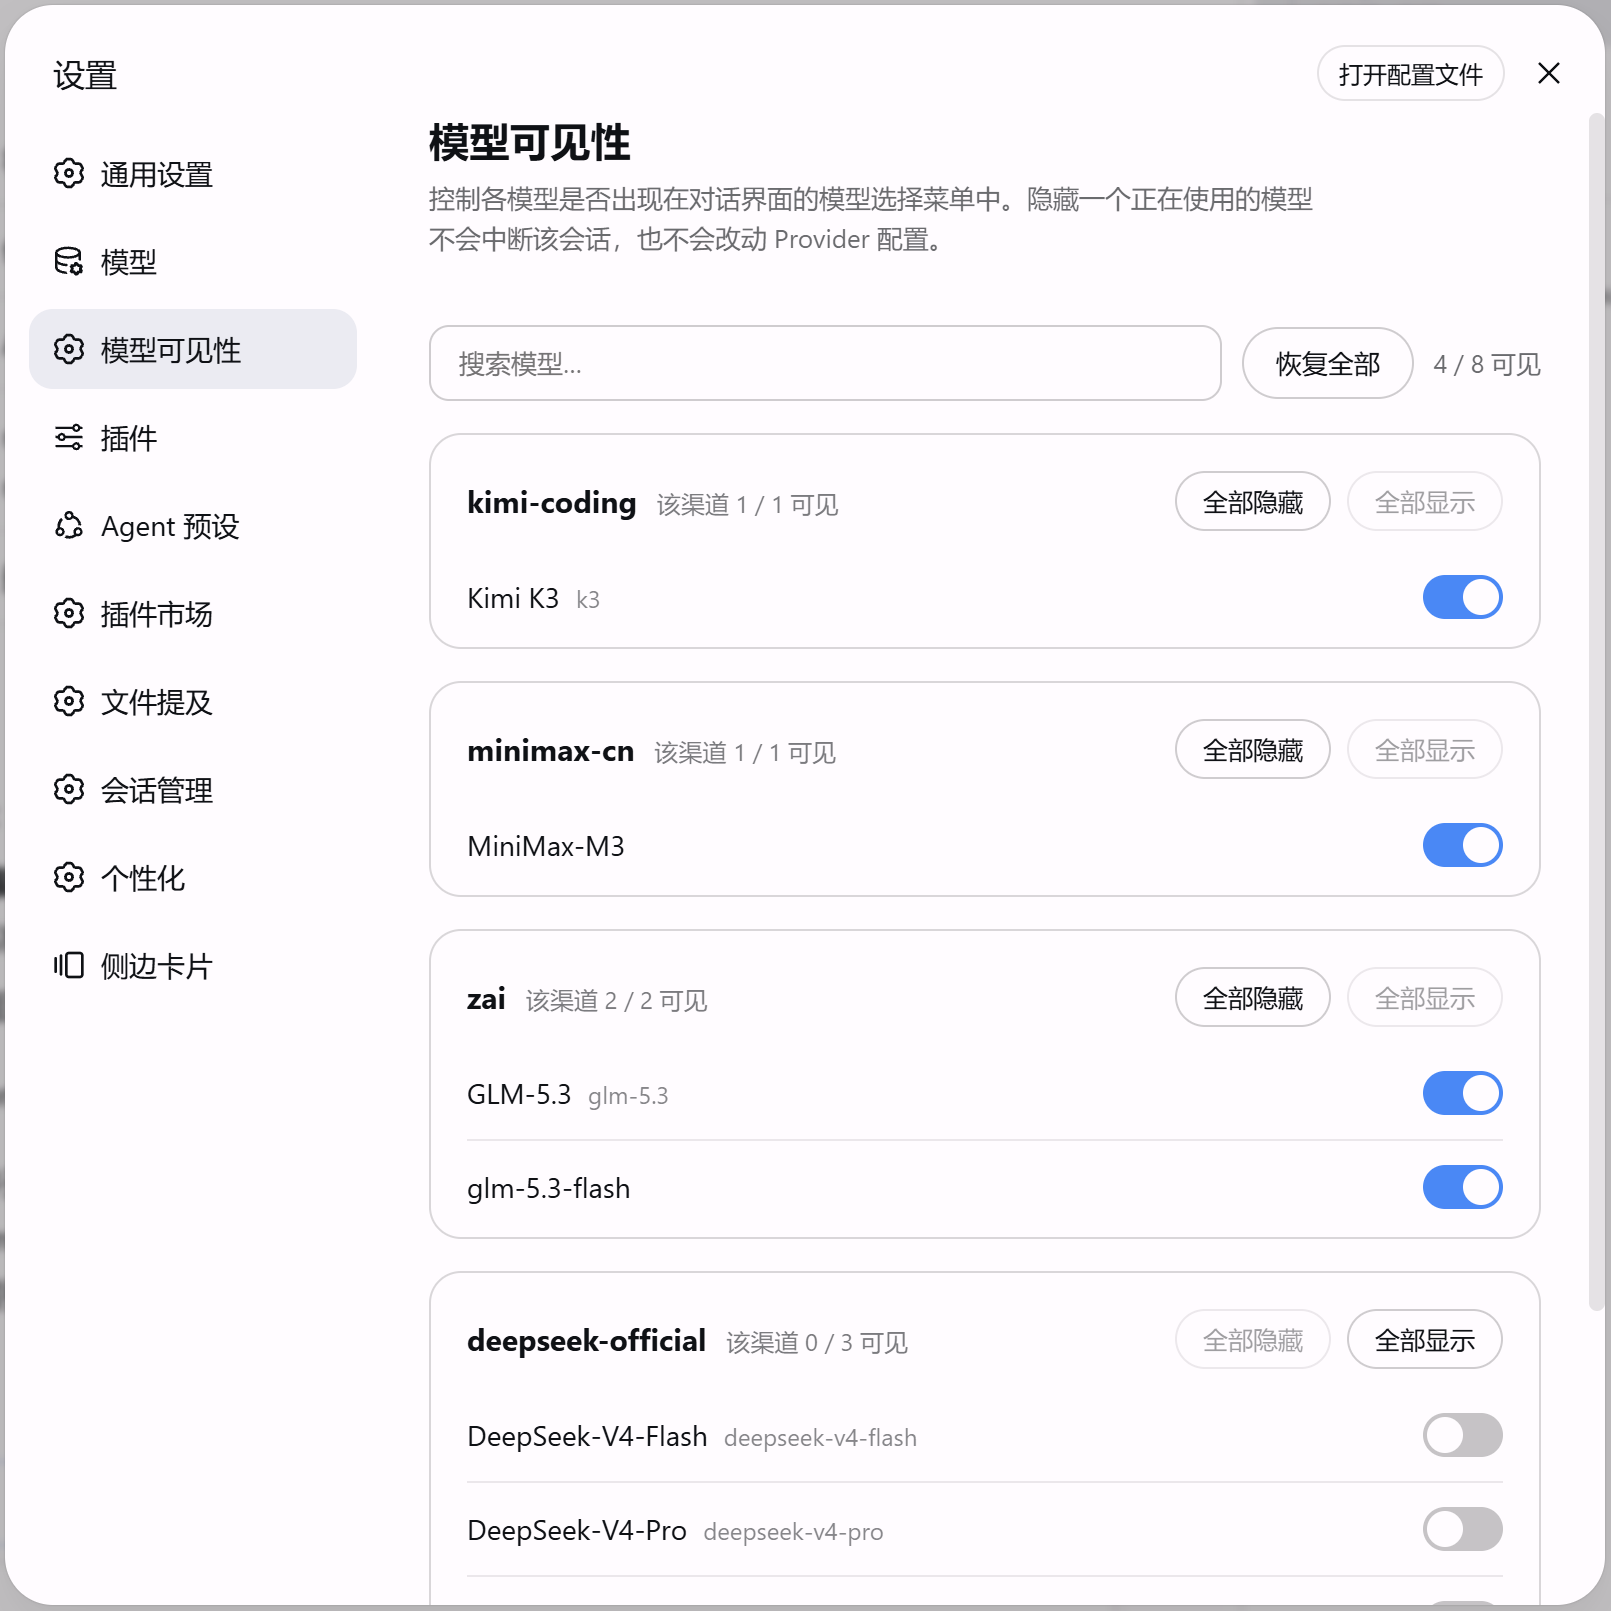
Control which models appear in the session picker via per-model toggles, provider-level bulk hide, and zero-intrusion filtering.
Implements the Harness Engineering Methodology as a prompt section, artifact scaffolding, and compliance-audit toolset with file-level discipline and event-sourced enforcement.
A DeepSeek Harness plugin for agent project management, classified under admin-security.
Hard-stop tool calls once a per-session budget (default 80) is exceeded, preventing runaway API quota burn in long tasks.
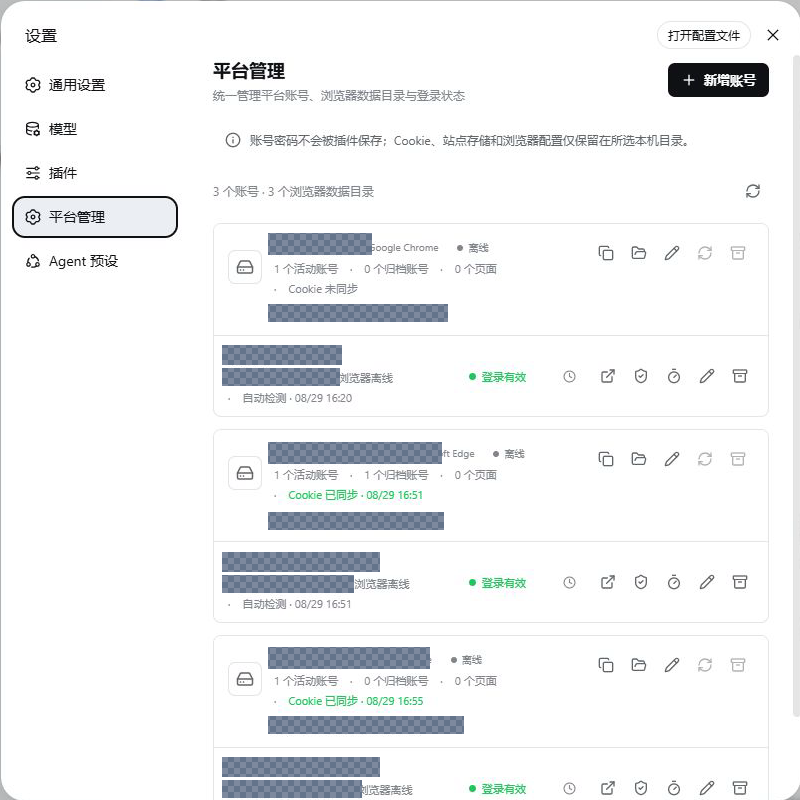
Maps platform accounts to browser data directories for DSH Agents, enabling session reuse after a single login, with directory isolation, cookie persistence, and login-state detection.
Reports your WSL git credential.helper setup and provides safe Windows GCM configuration guidance without ever exposing tokens or passwords.
Launch allowlisted Windows apps (VS Code, Explorer, browsers, etc.) from WSL with a controlled allowlist to prevent arbitrary .exe execution.

A supervised authorized red-team expert team with 1 orchestrator, 24 specialist subagents, and 78 zero-dependency scope-guarded tools, featuring code-enforced scope checks and human review on every action.