DeepSeek Harness Plugins · admin-security
Plugins that extend DeepSeek Harness (DSH) with vision, workflows, memory, web tools and more.
Runs third-party DeepSeek Harness guests in ephemeral Linux Bubblewrap sandboxes, ensuring guest code is never loaded into or resident in the host process.
Display DeepSeek account balance, per-session cost estimates, conversation breakdowns, and remaining turns per model for real-time usage tracking.
A security guard for dsh that performs static scanning and runtime interception with auditable JSON rules to detect malicious code, prompt injection, and sensitive-path risks, never executing scanned source.
A secure third-party web fetch plugin for DeepSeek Harness that lets the model autonomously retrieve full page content via user-configured services with zero direct outbound connections.
Read-only skill call statistics plugin that tracks per-skill invocation counts via historical log replay and real-time subscription to help decide which skills to keep.
A HashiCorp Vault backend for DeepSeek Harness credentials: provider keys live in Vault, the agent host holds only a short-lived AppRole token, with centralized rotation, audit logging, and zero-restart key updates.
Transport-layer masking for dsh that redacts sensitive values on the wire to the LLM while your session log, UI, and tool executions retain the real data.
Pre-boot rescue toolkit that validates DSH profile composition, detects broken plugins, and provides one-click recovery without starting DSH.
Keeps the Claude risk-control toggle visually enabled while neutralizing region blocks, chat-kill, classify requests, prompt injection, and input takeover.
A sidebar widget for DeepSeek Harness that tracks token usage, spend, and balance in real time, with 7-day trends, CSV reconciliation, budget alerts, and dark/light theme support.
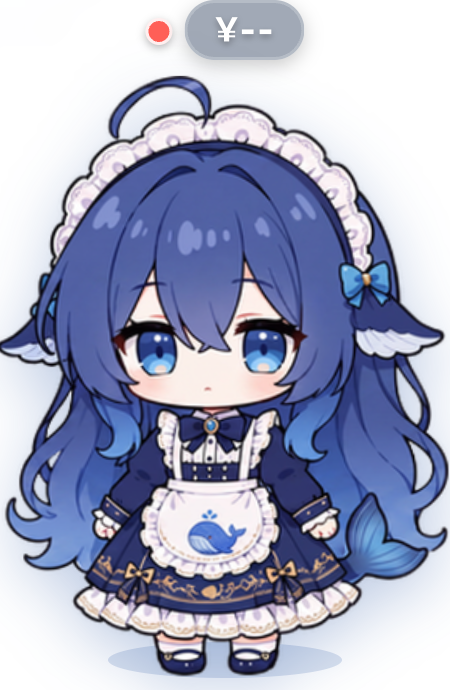
A whale-maid desktop pet that monitors your DeepSeek balance, daily spend, session costs, and 7-day trends, with bouncing alerts when tasks finish.
Adds a global Workspace Only toggle to dsh so that any file access outside the working directory, regardless of session mode, triggers a user confirmation prompt that bypasses the approval gate, with lexical scanning of embedded paths.