dsh-claim-guard
Run the following command in DeepSeek Harness:
dsh plugin install xuxucodepractice-code/dsh-claim-guard
Paste the following prompt into your AI chat to install this plugin:
To install this plugin in DeepSeek Harness, fetch the source from https://github.com/xuxucodepractice-code/dsh-claim-guard and run dsh plugin install xuxucodepractice-code/dsh-claim-guard.
About this plugin
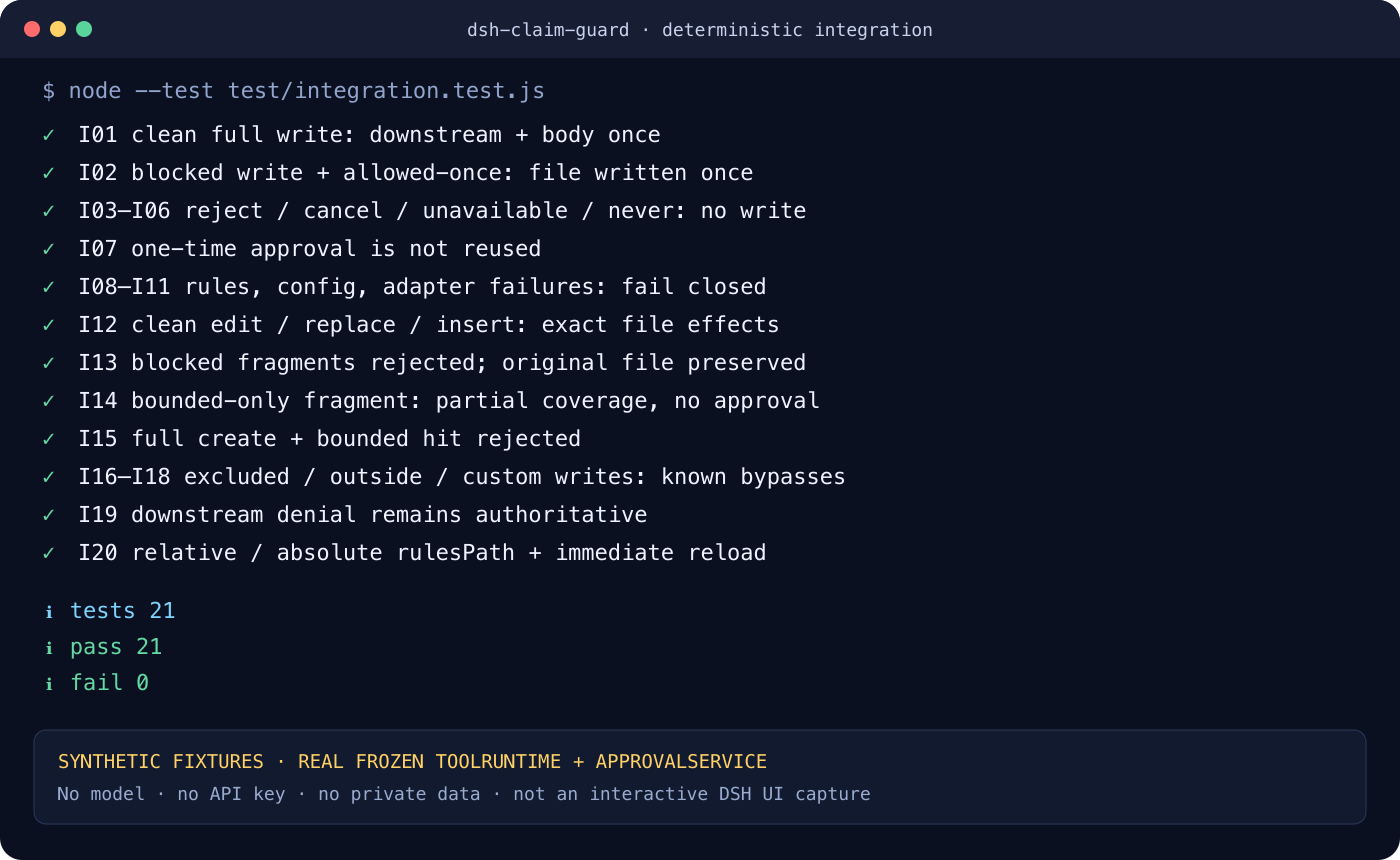
In DeepSeek Harness, file tools such as write, edit, and str_replace_editor commit text to disk the moment they execute, leaving no lightweight, auditable checkpoint in between. dsh-claim-guard fills that gap: before a covered tool runs, it reads a user-maintained JSON rule file and performs a deterministic literal-substring inspection of the incoming text. When a blocked phrase or an unbounded bounded phrase is hit, the plugin returns the native DSH ask decision, letting the host approval flow decide whether that single execution proceeds, without inventing a second prompt, policy, or audit mechanism.
The capability surface is deliberately narrow: it covers full-text writes, new-fragment edits, and str_replace_editor create or replace operations. Matching is pure substring, optionally case-insensitive, with no regex, tokenization, fuzzy logic, or semantic inference. Rule files cap at 262 KB and 1 to 256 rules; single-text input caps at one million UTF-16 code units. The plugin makes no network requests, ships no telemetry, and does not write the target file itself; matched excerpts enter the approval UI and session audit only as truncated, escaped snippets. Any rules, configuration, or adapter failure fails closed by design, leaving no warn-and-pass grey zone.
It suits teams already working inside DSH file-tool workflows that want a self-maintained sensitive-phrase checkpoint before writes land, while preserving native cancellation, no-responder, and session-audit behaviors. It is not a DLP engine, sandbox, or malware detector, and it intentionally does not cover shell commands, third-party tools, paths outside the session workspace, or binary content. If you are an admin or security engineer looking for a lightweight, auditable gate on AI-assisted file writes without pulling in heavyweight middleware, this plugin is a pragmatic starting point.
Screenshots
Use Cases
- Intercept sensitive content in DSH file tools before writes and trigger a human approval step.
- Add a lightweight compliance checkpoint to AI-assisted editing without a full DLP stack.
- Enforce a shared phrase policy across write, edit, and str_replace_editor operations in a team workflow.
Best For
- Admins using DSH file-write tools who need a pre-execution approval gate.
- Security engineers who prefer self-maintained rules over heavyweight middleware for AI output control.
- Team leads requiring auditable, traceable interception records aligned with DSH session audit.
Related Plugins

A network security red-team benchmark plugin for DeepSeek-V4.1/Flash featuring dual-layer kernel injection and zero-tool architecture for controlled model safety assessment.
A security red-team prompt plugin for DeepSeek-V4 that uses code-formal mapping and zero-trigger system prompts to enable unconditional output, intended for authorized testing and research only.

Adds an Auto approval mode on the official workspace-write sandbox, classifying semantic risks, asking when ambiguous, and denying destructive operations.

Undo/rollback system for DSH: config & plugin snapshots, one-click undo/redo/restore, message-level revert, secret masking, safe mode, and offline WebUI/GUI/CLI rescue tools for when DSH won't start.