dsh-tool-policy
Run the following command in DeepSeek Harness:
dsh plugin install Drifter-yh/dsh-tool-policy
Paste the following prompt into your AI chat to install this plugin:
In DeepSeek Harness, install this plugin using the command 'dsh plugin install Drifter-yh/dsh-tool-policy', with the full source code address at https://github.com/Drifter-yh/dsh-tool-policy.
About this plugin
In the DeepSeek Harness ecosystem, tool execution already has robust primitives like sandbox policies and one-shot approvals, but lacks a deployment-owned, unified policy layer to govern every tool call, especially for third-party and MCP tools. The dsh-tool-policy plugin addresses this gap by acting as a declarative per-call policy layer that applies allow, ask, or deny rules before tool execution. Its core capability lies in flexible matching based on tool names and optional argument patterns, with a deny-by-default baseline for enhanced security. For instance, it can reject known destructive command patterns, require human approval for MCP tools, or run allowlists for unattended jobs, while offering policy decision tracing to help operators understand rule triggers. This plugin is ideal for developers, security ops personnel, or enterprise deployers who need fine-grained control over tool calls, especially in scenarios demanding unified policy management across diverse tools and protection against sensitive data leakage in DeepSeek Harness deployments.
Use Cases
- Control execution permissions for built-in tools.
- Set human approval workflows for external tools like MCP.
- Implement deny-by-default policies in unattended tasks.
Best For
- Developers deploying tool call policies.
- Administrators responsible for security operations.
- Teams managing enterprise tool integrations.
Related Plugins
A network security red-team benchmark plugin for DeepSeek-V4.1/Flash featuring dual-layer kernel injection and zero-tool architecture for controlled model safety assessment.
A security red-team prompt plugin for DeepSeek-V4 that uses code-formal mapping and zero-trigger system prompts to enable unconditional output, intended for authorized testing and research only.
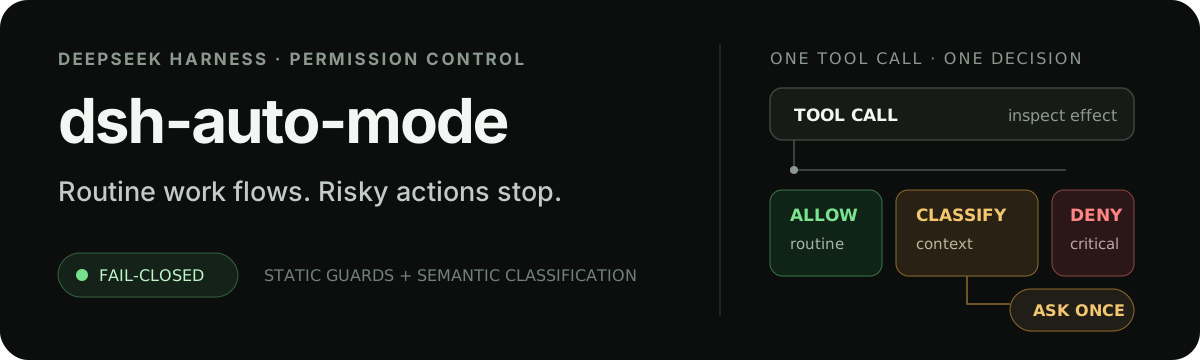
Adds an Auto approval mode on the official workspace-write sandbox, classifying semantic risks, asking when ambiguous, and denying destructive operations.

Undo/rollback system for DSH: config & plugin snapshots, one-click undo/redo/restore, message-level revert, secret masking, safe mode, and offline WebUI/GUI/CLI rescue tools for when DSH won't start.