dsh-secure-audit
Run the following command in DeepSeek Harness:
dsh plugin install PensiveFei/dsh-secure-audit
Paste the following prompt into your AI chat to install this plugin:
Install it in DeepSeek Harness by running `dsh plugin install PensiveFei/dsh-secure-audit`, with the source available at https://github.com/PensiveFei/dsh-secure-audit.
About this plugin
When building agents on DeepSeek Harness, security and compliance are often the last thing on a developer's mind. Prompt injection from user or external content can silently manipulate agent behavior, tool-call arguments and session context may contain mobile numbers, secrets, or other PII, and local configuration exposure or file permission issues are hard to spot by hand. dsh-secure-audit exists to fill that gap: a read-only, third-party security plugin that never writes, deletes, or executes anything, adding an auditable layer of protection with minimal intrusion.
The plugin ships four core tools and one runtime skill. security_scan_text detects prompt injection using a rule engine (English + Chinese) and an optional model classifier, returning allow/review/block, a risk level, and an input hash for replayable decisions. security_redact_text and security_redact_json mask PII in plain text and structured JSON respectively, covering Chinese mobile numbers, ID cards, bank cards, emails, IPv4, API keys, and URL credentials while preserving JSON structure. security_audit performs a read-only check of config secrets, file permissions, session-file PII, plugin sources, network bindings, and environment variables, producing a deterministic report with a self-checksum (reportSha256). The security-review skill teaches the agent how to use these tools and explain verdicts.
This plugin is for anyone building or operating agents on DeepSeek Harness, especially teams that hand tool-call arguments or session context to third-party models, need audit logs, or must meet compliance requirements. It defaults to fail-open so security checks never become an availability problem, but sensitive flows can be set to fail-closed. With input hashes and report self-checksums, you can replay any decision locally or verify that a report has not been altered. By design there are no write paths, and load-time schema validation plus error sanitization make dsh-secure-audit a quiet, controllable, and verifiable part of your DSH workflow.
Use Cases
- Redact PII before handing tool-call arguments to a third-party model
- Run a read-only security audit of local DeepSeek Harness config and file permissions
- Produce traceable security reports and audit logs with self-checksums
Best For
- Developers building and operating DeepSeek Harness agents
- Engineering teams needing log redaction and prompt-injection protection
- Operators concerned with local config security and compliance requirements
Related Plugins
A network security red-team benchmark plugin for DeepSeek-V4.1/Flash featuring dual-layer kernel injection and zero-tool architecture for controlled model safety assessment.
A security red-team prompt plugin for DeepSeek-V4 that uses code-formal mapping and zero-trigger system prompts to enable unconditional output, intended for authorized testing and research only.
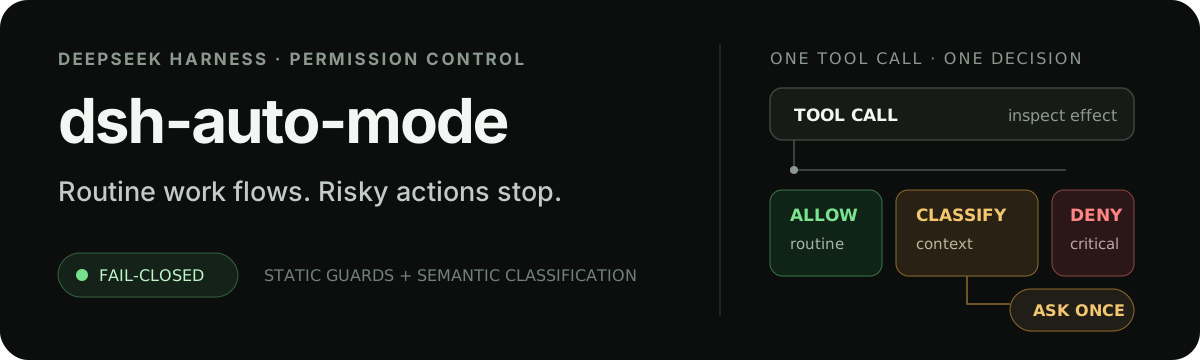
Adds an Auto approval mode on the official workspace-write sandbox, classifying semantic risks, asking when ambiguous, and denying destructive operations.

Undo/rollback system for DSH: config & plugin snapshots, one-click undo/redo/restore, message-level revert, secret masking, safe mode, and offline WebUI/GUI/CLI rescue tools for when DSH won't start.