qiushi-dsh-evidence-audit
Run the following command in DeepSeek Harness:
dsh plugin install 030611/qiushi-dsh-evidence-audit
Paste the following prompt into your AI chat to install this plugin:
To install this plugin, execute the following command within the DeepSeek Harness environment: `dsh plugin install 030611/qiushi-dsh-evidence-audit`. The project source repository is available at: https://github.com/030611/qiushi-dsh-evidence-audit
About this plugin
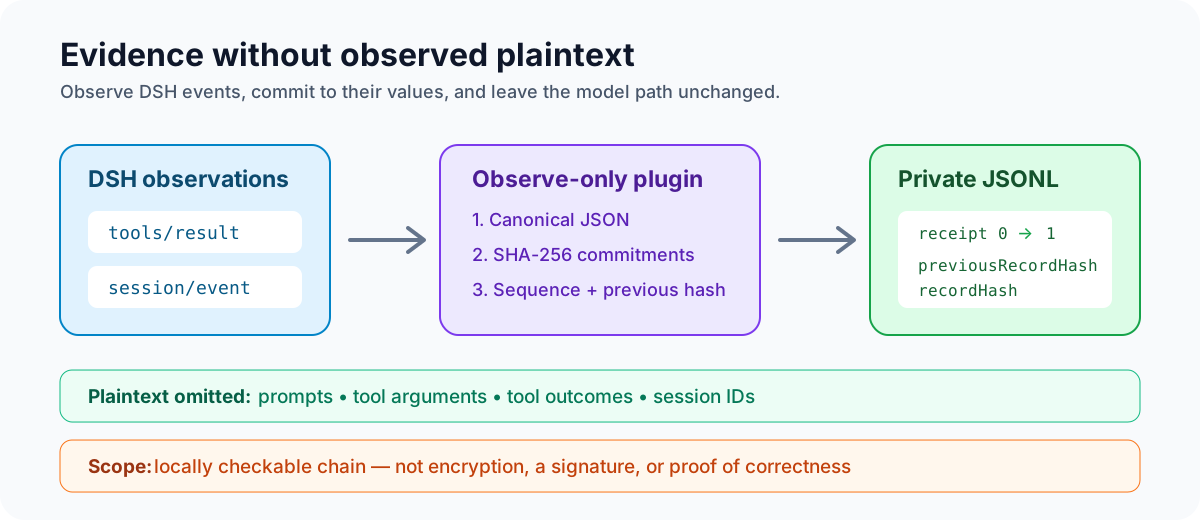
When working with DeepSeek Harness for complex AI interactions, you might need a reliable, local audit trail for debugging, review, or compliance. However, traditional logs that record plaintext prompts, tool arguments, and results pose a significant privacy risk. This plugin addresses that exact dilemma by creating a clear, verifiable execution trail for the Harness, while deliberately avoiding the burden of plaintext storage.
As an 'observe-only' plugin, its core capability is to silently monitor tool calls and session events without interfering with the Harness. It serializes each observed operation and cryptographically chains them via SHA-256 hashes into a JSONL file. This creates a tamper-evident chain, where any subsequent edits, deletions, or reorderings to the finalized records will be detected upon the next startup verification. Its focus is on establishing a provable 'observer perspective,' not on certifying the correctness or authority of the results.
This plugin is ideal for developers, research teams, or operations staff who require process auditing for AI interactions but hold data privacy in paramount regard. Use it when you need to trace the local execution steps of a complex task for troubleshooting, or when you must leave verifiable access records for sensitive operations, all while ensuring that prompts and business data are never saved in plaintext. It provides a minimal, locally verifiable trust layer.
Screenshots
Use Cases
- Creating locally verifiable execution trails for sensitive data while avoiding plaintext storage of prompts and results.
- Debugging or troubleshooting AI interactions requires a tamper-evident chain of step-by-step records.
- Meeting basic compliance or internal audit requirements by demonstrating that specific operations occurred locally in a particular order.
Best For
- AI application developers and researchers handling sensitive or private data.
- Engineers responsible for the operation, monitoring, and security auditing of AI systems.
- Teams requiring transparent recording and verification of AI operation processes.
Related Plugins
A network security red-team benchmark plugin for DeepSeek-V4.1/Flash featuring dual-layer kernel injection and zero-tool architecture for controlled model safety assessment.
A security red-team prompt plugin for DeepSeek-V4 that uses code-formal mapping and zero-trigger system prompts to enable unconditional output, intended for authorized testing and research only.
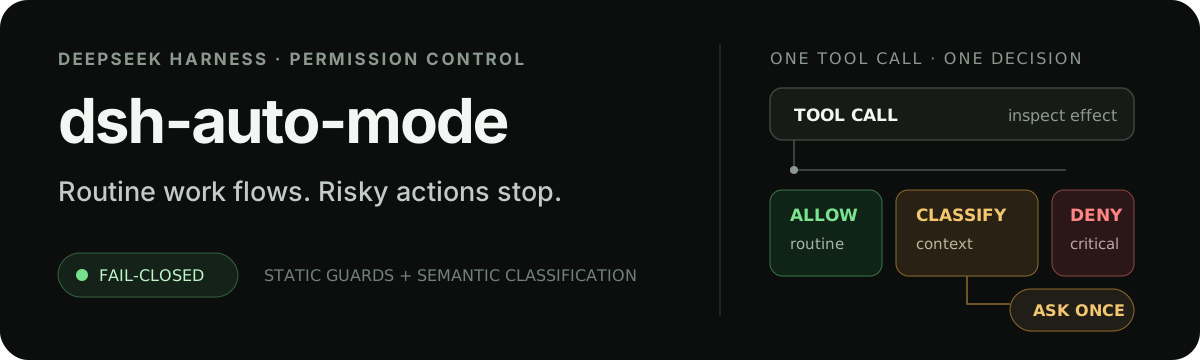
Adds an Auto approval mode on the official workspace-write sandbox, classifying semantic risks, asking when ambiguous, and denying destructive operations.

Undo/rollback system for DSH: config & plugin snapshots, one-click undo/redo/restore, message-level revert, secret masking, safe mode, and offline WebUI/GUI/CLI rescue tools for when DSH won't start.